BLA: An open-source Blue Team defence MCP plugin that equips software with "AI reverse engineering protection" armourBLA:给软件穿上「防 AI 逆向」护甲的开源蓝方防御 MCP 插件
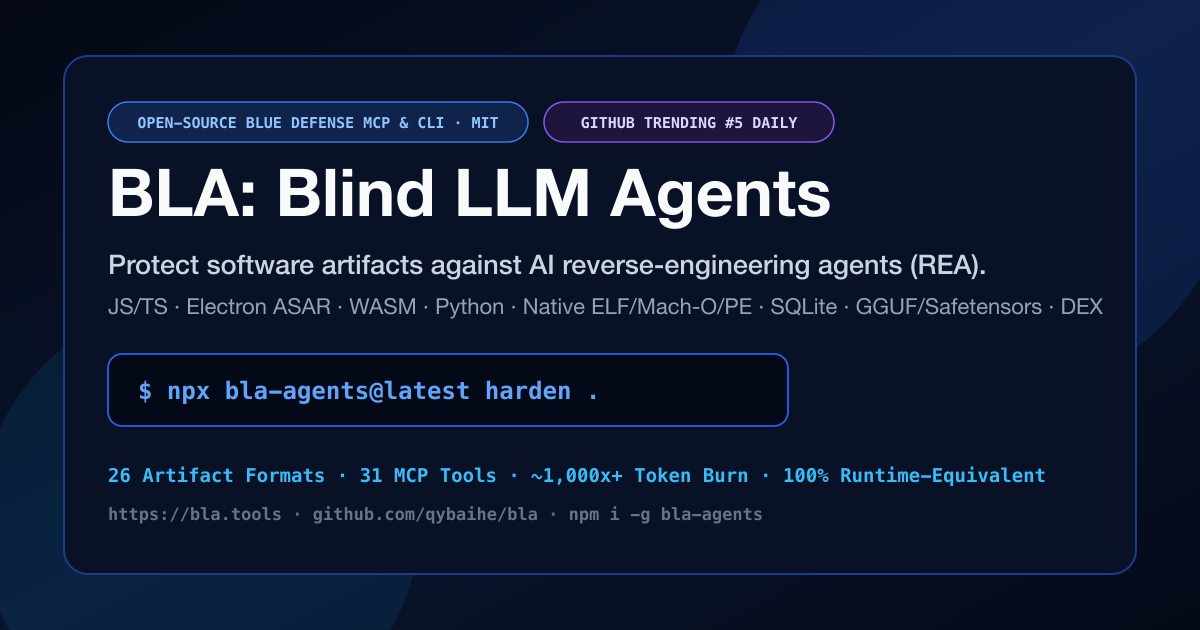
An AI Reverse Engineering Agent (REA) can tear apart a release package in just a few minutes, while the defenders are still using obfuscators from the last century. BLA (Blind LLM Agents) is an open-source blue team defence MCP & CLI that rose to 5th place on the GitHub Trending daily list this week: 31 defence tools covering 26 product formats, using the three-pronged approach of "poisoning → exhaustion → hallucination" to bankrupt AI reverse engineering in terms of computing power.
AI 逆向 Agent(REA)几分钟就能把一个发布包拆个底朝天,防御方却还在用上世纪的混淆器。BLA(Blind LLM Agents)是本周冲上 GitHub Trending 日榜第 5 的开源蓝方防御 MCP & CLI:31 个防御工具、覆盖 26 种产物格式,用「投毒 → 耗尽 → 幻觉」三板斧让 AI 逆向在算力上破产。
What does it protect against?它防的是什么
Your JS/TS, Electron ASAR, WASM, Python, native binaries, SQLite, GGUF/Safetensors, and even Android DEX are no longer just facing human reverse engineers – AI reverse engineering agents like morluto/rea, autonomous decompilers, and LLM reconnaissance pipelines will automatically read symbols, trace call chains, and reconstruct logic, and after a few iterations, they'll spit out readable source code.
The idea behind BLA is to exploit the weaknesses of LLMs in reverse: by injecting decoy symbols, contextual baits, and redundant branches into the output, the reverse Agent consumes a thousand times more tokens from its budget. Ultimately, the outputted "source code" contains numerous hallucinations and does not align with runtime behaviour. The author team empirically validated this effect on 14 benchmark targets, and the hardened output demonstrated 100% runtime equivalence.
This week, the project ranked 5th on GitHub Trending's daily list. The npm package bla-agents has been updated to v3.5.1, and is open-source under the MIT licence. The official website, bla.tools, provides defence guidelines, real-time benchmarks, and a CrackMe arena.
你的 JS/TS、Electron ASAR、WASM、Python、原生二进制、SQLite、GGUF/Safetensors 乃至安卓 DEX 发布出去,面对的不再只是人类逆向工程师——morluto/rea 这类 AI 逆向 Agent、自主反编译器和 LLM 侦察流水线会自动读符号、追调用链、还原逻辑,几轮迭代就能吐出可读源码。
BLA 的思路是反向利用 LLM 的弱点:往产物里注入诱饵符号、上下文毒饵和冗余分支,让逆向 Agent 消耗上千倍的 token 预算,最后输出的「源码」大量幻觉、与运行时行为对不上——作者团队在 14 个基准目标上实测验证了这套效果,且加固后的产物 100% 运行时等价。
项目本周拿下 GitHub Trending 日榜第 5,npm 包 bla-agents 已迭代到 v3.5.1,MIT 开源,官方站点 bla.tools 提供防御指南、实时基准和 CrackMe 竞技场。
Two Ways to Use the MCP Plugin and CLIMCP 插件与 CLI 两种用法
The CLI mode is the fastest: After npm i -g bla-agents, run npx bla-agents@latest harden . in the project directory.It will scan the directory for protectable artefact formats and harden them one by one, producing a report describing what was done to each file.
MCP mode is for users of Agents such as Claude Code, Codex, and Cursor: After connecting BLA as an MCP server, 31 defence tools are directly added to the Agent toolbar, allowing you to harden and perform health checks on individual files, ASAR packages, or Safetensors weights as needed during development sessions.
Maximum security attributes: The hardening operation only modifies the release artefacts and not the source code. When combined with CI, "automatic hardening after build" can be achieved. The official documentation also provides specific guidelines for Electron applications and Python packages.
CLI 模式最快:npm i -g bla-agents 后,在项目目录执行 npx bla-agents@latest harden .,它会扫描目录里可保护的产物格式并逐个加固,产出报告说明每个文件做了什么处理。
MCP 模式面向 Claude Code / Codex / Cursor 等 Agent 用户:把 BLA 接成 MCP 服务器后,31 个防御工具直接挂进 Agent 工具栏,可以在开发会话里按需对单个文件、ASAR 包或 Safetensors 权重做加固与体检。
安全属性拉满:加固操作只改发布产物不改源码,配合 CI 可以做到「构建后自动加固」,官方文档还给了针对 Electron 应用和 Python 包的专项指南。
Download and Get Started下载与上手
Click the button above to download bla-agents-3.5.1.tgz (1.02MB, official npm tarball). Offline installation: npm install -g ./bla-agents-3.5.1.tgz; for online installation, simply use npm i -g bla-agents.
After installation, first run bla --version to confirm, then run npx bla-agents@latest harden . on a test directory. Check the hardening report. If you want to understand the principles of defence, the Chinese guide on the official website bla.tools/guides is very clearly written.
Be mindful of compliance boundaries: The BLA is intended to protect your own released products. Do not use it to strengthen software that does not belong to you. There is a dedicated DISCLAIMER page in the repository that explains this boundary.
点上方按钮下载 bla-agents-3.5.1.tgz(1.02MB,npm 官方 tarball)。离线安装:npm install -g ./bla-agents-3.5.1.tgz;在线安装则直接 npm i -g bla-agents。
装完先跑 bla --version 确认,再对一个测试目录执行 npx bla-agents@latest harden . 看加固报告;想了解防御原理,官方站 bla.tools/guides 的中文指南写得非常清楚。
注意合规边界:BLA 用于保护你自己的发布产物,不要拿去加固不属于自己的软件——仓库里专门有 DISCLAIMER 页说明这条红线。
Note小提示
BLA's defence is a probabilistic game rather than absolute encryption: it significantly increases the cost of reverse engineering and corrupts the results of reverse engineering, and works best when combined with conventional obfuscation and legal measures. When evaluating, you can directly run the official CrackMe arena and use a real REA Agent to run through it once to see the token consumption curve. The official BLA npm package that accompanies this article can be found via the download button above.
BLA 的防御是概率博弈而非绝对加密:它显著抬高逆向成本、污染逆向结果,配合常规混淆和法律手段使用效果最好。评估时可直接跑官方 CrackMe 竞技场,用真实 REA Agent 打一遍看 token 消耗曲线。本文配套 BLA npm 官方包见上方下载按钮。
⬇ Download · 点击下载:BLA(bla-agents)v3.5.1 官方 npm 包
MIT · npm 官方 tarball · npm i -g bla-agents 或 npx bla-agents@latest harden . 一条命令加固
阅读与点赞数据保存在你的浏览器本地,欢迎留下你的想法。
 今日正能量学一点,用一点;今天种下的种子,会长成明天的能力。去免费下载专区 →广告
评论 文明发言,让讨论更有价值